If you run a website on WordPress, Joomla, Drupal, or another PHP-based platform, it’s worth paying attention to a new warning from cybersecurity experts. Two critical security holes have been found in the popular programming language. They could potentially let attackers get into servers, steal data, or wreak havoc on websites.
AI bot activity can create a load the site was not prepared for
Imagine the situation: in the morning, the hosting control panel greets you with an availability error notification, while the pages themselves open with a noticeable delay. The statistics are silent, ad campaigns are not running, and there is no spike in real visitors. Most likely, the reason lies in invisible visitors – bots that scan content for training neural networks.
A server hack is not always immediately noticeable
The website has slowed down, even though visitor numbers haven’t gone up. The CPU stays busy at night, unfamiliar messages keep appearing in the mail queue, and the provider reports suspicious requests from the server’s IP address. The first assumption is usually simple: something has broken. But it may be more serious than that. A server can still look perfectly normal while somebody else is already using it to send spam, attack other systems, or reach stored data.
Phishing often starts with trusting a familiar name
You receive an email from a bank, mobile operator, service provider, or business partner. It says that a payment is overdue, your password is about to expire, or your account will soon be suspended. There is usually a button and a request to act right away. Everything may look familiar, including the logo and layout. Even so, it is worth stopping for a moment and checking who really sent the message.
Sometimes a website starts behaving as if it is under a heavy DDoS attack: pages open slowly, the API responds with delays, 502 or 503 errors appear in the logs, and web server processes suddenly start consuming much more memory. But at the same time, there is no huge stream of requests, the channel is not saturated, and the load may come from a small number of connections. This is how HTTP/2 Bomb works. It is a DoS attack on HTTP/2 – the protocol through which a website or application exchanges data with the server. The attacker sends a relatively small amount of data but forces the server to spend much more memory processing it. As a result, the web server or proxy may freeze, start using disk instead of RAM, restart processes, or stop serving regular users properly.
Within a closed circle, a new AI model called Claude Mythos is being tested, described as significantly “smarter” than the company’s previous solutions. The emergence of this model confirms a trend: developers are releasing increasingly powerful neural networks while at the same time acknowledging their toxicity for digital security. Limited access is only an attempt to hold back the flow, because each new generation of algorithms automatically becomes a tool for finding holes in software or network infrastructure.
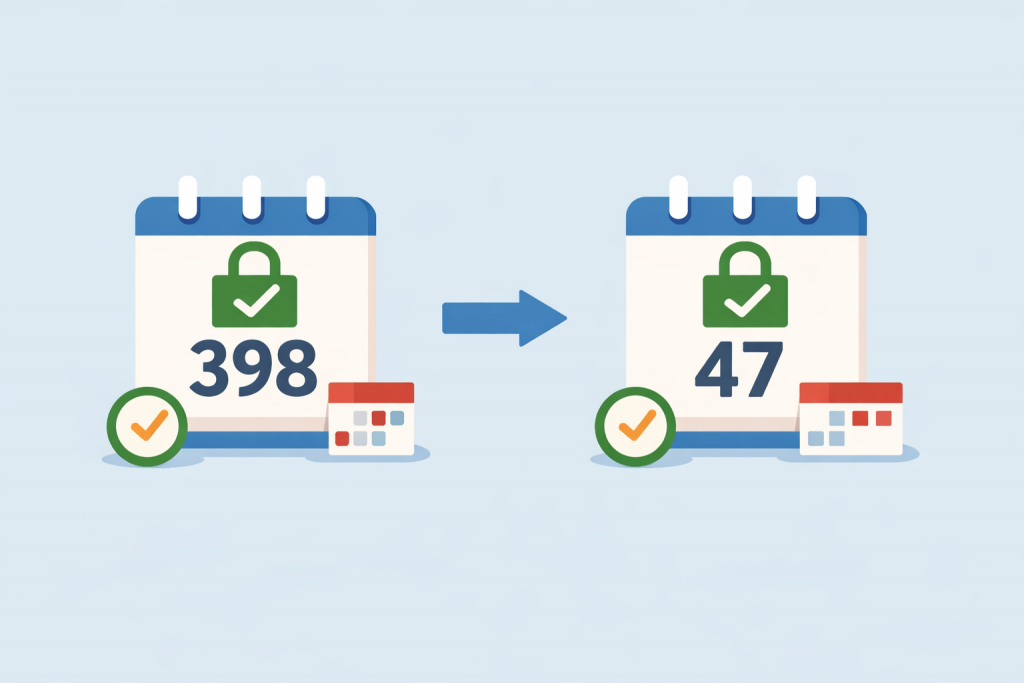
Until recently, an SSL certificate was perceived as a routine service: you paid once a year, configured it, and remembered it the next season. However, the security industry is steadily moving toward a point where the notion of a “year-long” certificate will disappear. Website owners will have to get used to a much more dynamic rhythm.
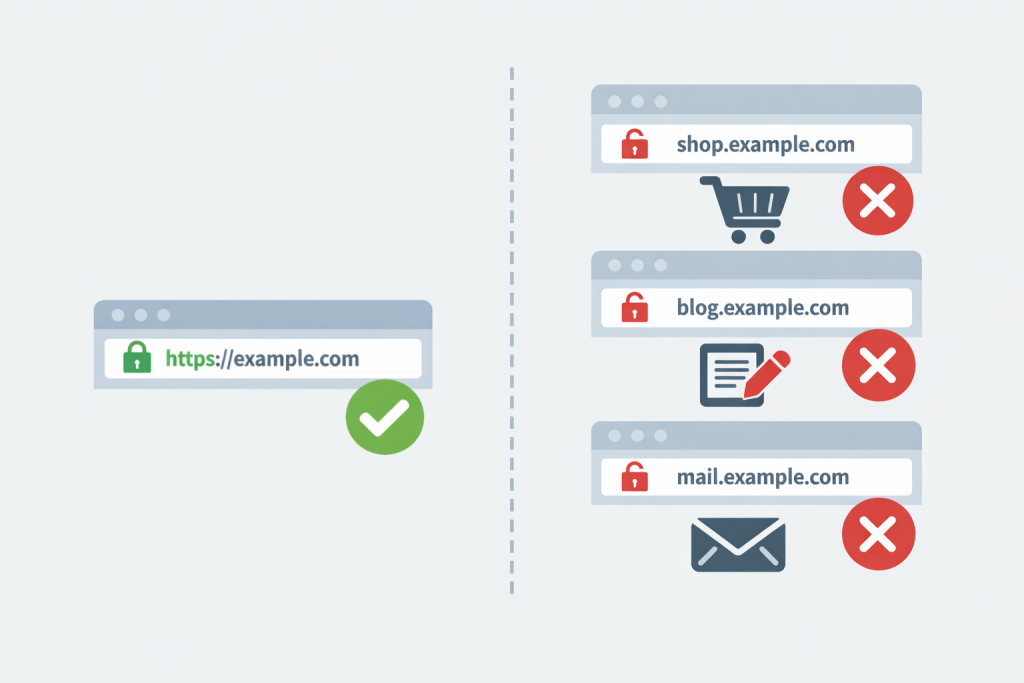
SSL doesn’t always automatically extend to subdomains
The situation is familiar to many website administrators. The main domain opens normally: the lock icon is visible in the browser, HTTPS works, there are no warnings. But as soon as you switch to a subdomain – for example blog.example.com or mail.example.com – the browser suddenly shows a message about an unsafe connection. For the user this looks like a website error. In reality, in most cases the server itself works normally. The issue is usually hidden in the way the certificate was issued or connected.
Backup is a single way to update access to digital assets
Cryptocurrency is often perceived as something ephemeral that lives “on the internet.” Because of this, a dangerous illusion appears: as if access to coins could be restored through email or technical support, like a regular password. In practice, the logic of how wallets work is fundamentally different. There is no administrator here who can reset settings or confirm your identity using a passport. A backup is not simply a “plan B,” but the only and final way not to lose money forever.
Different browser approaches to assessing the security of an encrypted connection
When a user opens a website and sees a padlock icon in the browser, it is perceived as a simple and clear signal of security. However, behind this symbol lies a complex SSL certificate verification mechanism that is triggered every time a secure connection is established. It is important to understand that different browsers may implement this verification differently. While the basic security principles are shared, specific trust policies and responses to errors vary, and this often explains why the same website behaves differently in different browsers.